Built inside the legal world
Former attorney experience and legal-institution technology leadership shape how we frame risk and next steps.
Who we are
Tyson Benson practiced law for fifteen years before moving into cybersecurity. R.B.C. managed IT and security operations inside a legal institution before advancing to CISO. That inside perspective changes how we assess risk: not just whether systems run, but whether your decisions are defensible when clients, insurers, or regulators ask hard questions.
Former attorney experience and legal-institution technology leadership shape how we frame risk and next steps.
No software resale, no license incentives, and no referral fees that distort the advice.
Findings are documented in plain language so firm leadership can act, explain, and follow through.
You know what we are reviewing, what access is needed, and what the engagement produces before work begins.
Most firms come here wanting one answer first: whether the advice will be practical, independent, and understandable to leadership.
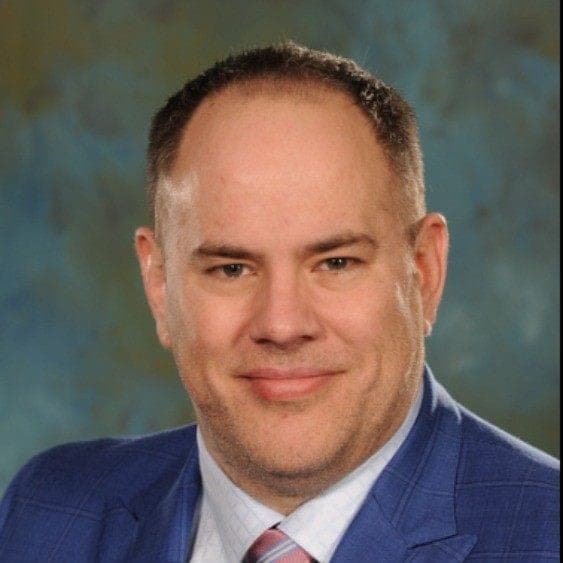
Former practicing attorney who understands how legal work flows, how clients are protected, and what bar ethics obligations actually require – not as an abstraction, but from the inside.
Transitioned fully into cybersecurity six years ago, bringing a perspective no generic IT firm can replicate: legal risk judgment combined with technical security practice.
Directly bridges the gap between the security recommendations you receive and the professional obligations, client expectations, and insurance questionnaires your firm faces every day.

Technical Security Lead
14 years in cybersecurity · 18 years across the full IT stack · served as IT Director inside a legal institution
Author of the popular G3tSyst3m's Infosec BlogCareer built from the ground up – starting as a web developer and network engineer, advancing through Director of IT, Senior Information Security Analyst, Director of Cybersecurity, and CISO.
Served as IT Director for a legal institution, overseeing technology and security operations in an environment governed by the same professional obligations, data sensitivity, and workflow pressures that define a law firm – this is not a theoretical familiarity.
Brings C-suite security leadership experience to engagements that are typically out of reach for small and mid-sized law firms – the same judgment a large firm pays a CISO for, applied at your scale.
How we work
Tyson practiced law for fifteen years. R.B.C. managed IT and security operations inside a legal institution. This practice is not a generic IT playbook applied to law firms – it was built by people who have operated inside them. Every deliverable is designed around bar ethics obligations, client questionnaire requirements, and how legal work actually flows.
Our approach treats security controls the way a court treats evidence: documented, verified, and provable. Controls are not assumed to be in place – they are tested, recorded, and reported with before-and-after evidence you can show to clients, insurers, or auditors.
We don't sell software, resell Microsoft licenses, or take referral fees. Our only interest is giving you an accurate picture of where you stand and closing the gaps that matter.
You'll know exactly what we're doing, what access we need, and what you receive at the end, before work begins. Engagements are fixed-scope, not open-ended.
Recognition & perspective
Recognized by Automotive IQ among the industry’s most influential voices on vehicle security and software risk.
View detailsFeatured in a RunSafe Security webinar on compliance, governance, and what really reduces exploitability in complex systems.
View detailsSpoke to the Iowa State Bar on protecting client data, cyber risk, and the practical safeguards law firms actually need.
View detailsWork with us
2 minutes. No internal access. No passwords.
The review is passive and takes minutes. If it shows gaps worth addressing, we'll walk through what an engagement looks like, with no pressure.